Your authorization
Agree assets and limits before any test.
For security and product teams worldwide: validate risks across your applications and APIs, give engineers reproducible evidence, and verify every fix.
Join the pilotSee how it works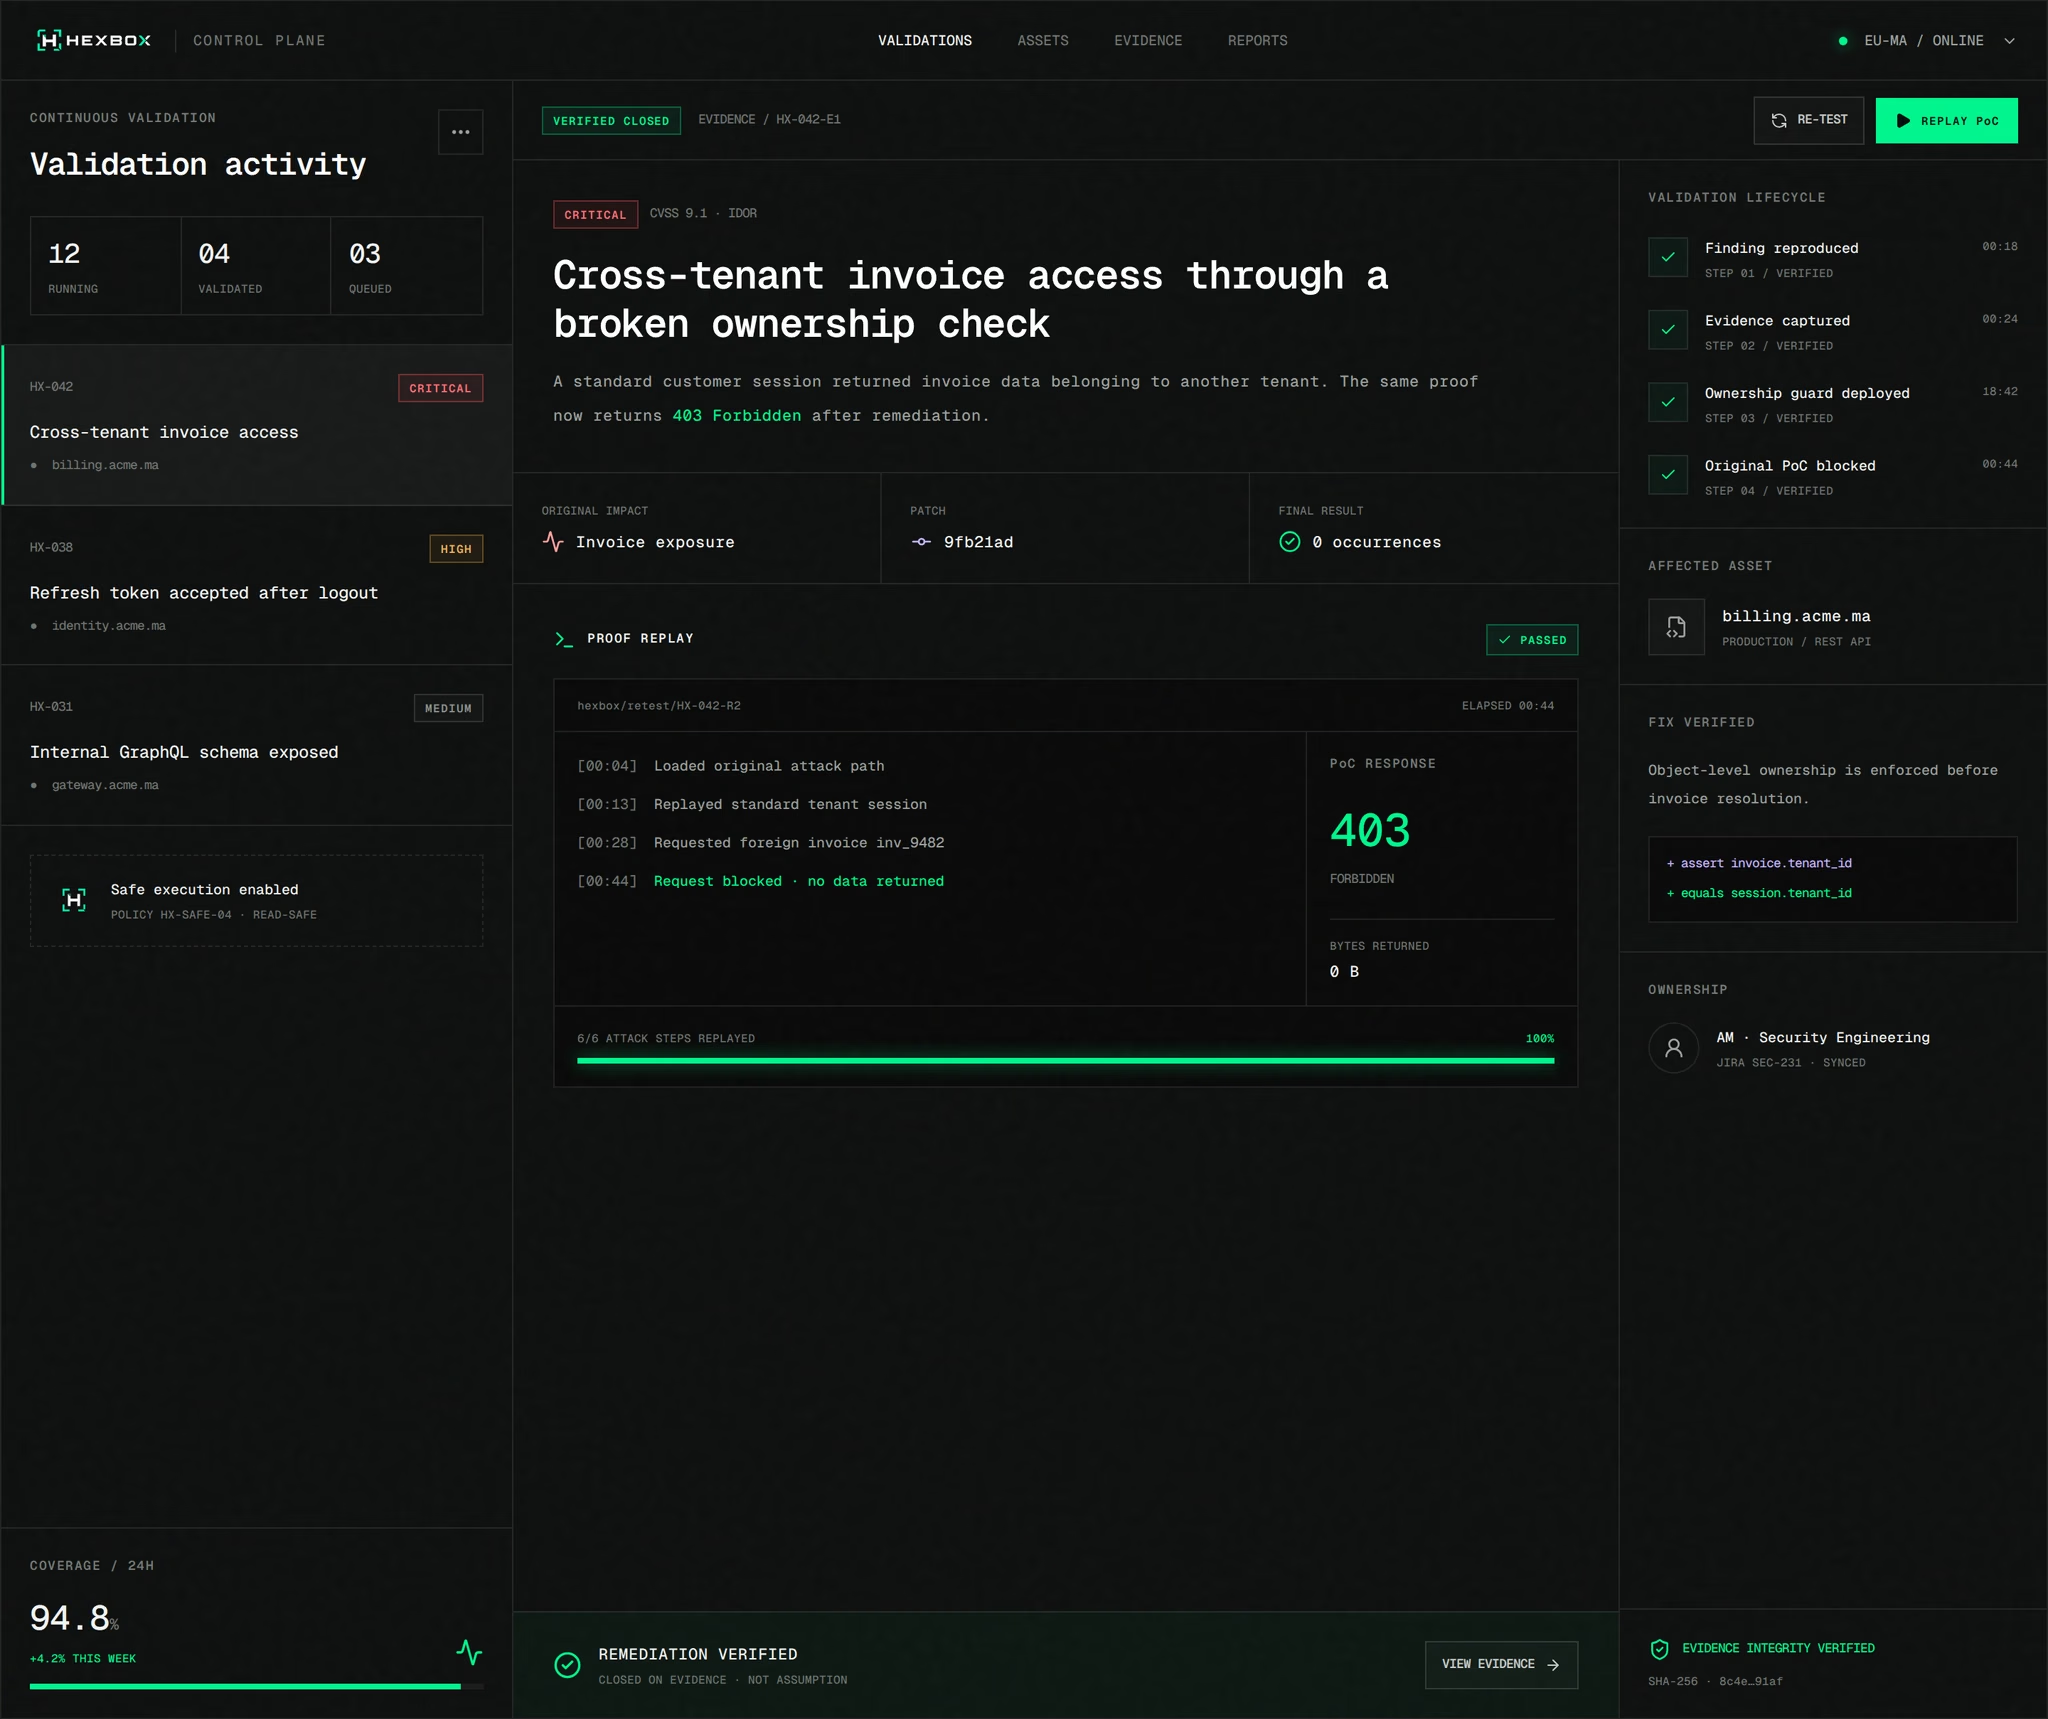
Validation across your attack surface
[THE CONCEPT]
One continuous loop, from your first test to a verified fix.
Together, we agree which assets can be tested, the limits, and when to stop.
Web app + API · authorized test accounts
Agree assets and limits before any test.
Agree access, evidence handling, and retention.
Define contacts and a stop procedure in advance.
[WHY HEXBOX]
Security should keep pace with your business. Here is what HexBox changes for your team.
Get initial results in hours on the agreed scope. Your team can start fixing issues sooner.
A one-off test shows security at one moment. HexBox checks over time and retests vulnerabilities after they are fixed.
Automation lowers the cost of repeated checks. Test more often without commissioning a new manual engagement each time.
Scope your applications and APIs with our team remotely. Share evidence your security and product teams can act on, wherever they work.
For each confirmed vulnerability: what was tested, how to reproduce the issue, and the retest result after remediation.
See it on your own scope[WHY CONTINUOUS TESTING]
When a one-time pentest ends, testing stops. New weaknesses can go unnoticed until the next assessment.
Engagement ends. Testing stops.
Repeated testing + verified fixes
The engagement ends with a report. Testing stops here.
The report is a starting point. Repeat testing within the agreed scope.
Shorter gaps without validation, rather than waiting for the next pentest.
Comparison of a one-time pentest without follow-up. Hexbox’s testing frequency is agreed within your authorized scope.
[ENGAGEMENTS]
AI pentesting and continuous validation for teams worldwide. Quotes in USD, with scope tailored to your web applications and APIs.
Understand your exposure and decide what to fix first.
Custom quote in USD
Keep testing as your application changes, and verify your fixes.
Custom quote in USD
Before starting: agree the scope, duration, and success criteria together. Scope, billing terms, and applicable taxes are confirmed in your quote.
[FAQ]
Scope, evidence, and safety. The essentials in six answers.
Web applications, APIs, identities, cloud exposure, and the attack paths connecting them — within an explicitly agreed scope.
No. Scanners surface possibilities. HEXBOX safely validates whether a path is genuinely exploitable and records the proof.
We monitor agreed surfaces, validate meaningful changes, deliver evidence, and retest fixes on a defined cadence.
Every engagement uses explicit scope, controls, limits, isolation, and a documented stop process.
Security and engineering teams that need stronger prioritization, reproducible proof, and verified remediation.
Yes. Scoping and collaboration happen remotely in English or French. We agree the scope, access, testing cadence, and commercial terms together, with a quote in USD.
[THE FOUNDING TEAM]
Four complementary disciplines. One shared standard: building security that can be demonstrated.


[YOUR NEXT STEP]
Make offensive security continuous, evidence-driven, and ready to act on.
Talk to HEXBOXTell us about your assets, priorities, and the scope you want to validate.